





















01
Necessary Always on
Required for the site to work (login, preferences, security). Always on.
OpenAI pointed its Astra model at its own systems and mobilized 250-plus staff to find and fix vulnerabilities before attackers get the same capability. Here's the MSP governance angle.
OpenAI has built what it calls a Defense Factory: an internal operation that uses its own AI agents, powered by a security-focused model called Astra, to continuously find and fix vulnerabilities in its systems before external attackers can. The company describes it as a response to a specific, narrowing advantage — what it calls the “defender's window,” the period during which defenders have direct access to their own source code and infrastructure plus early access to advanced models, before similar cyber capability becomes widely available to attackers through open-weight models.
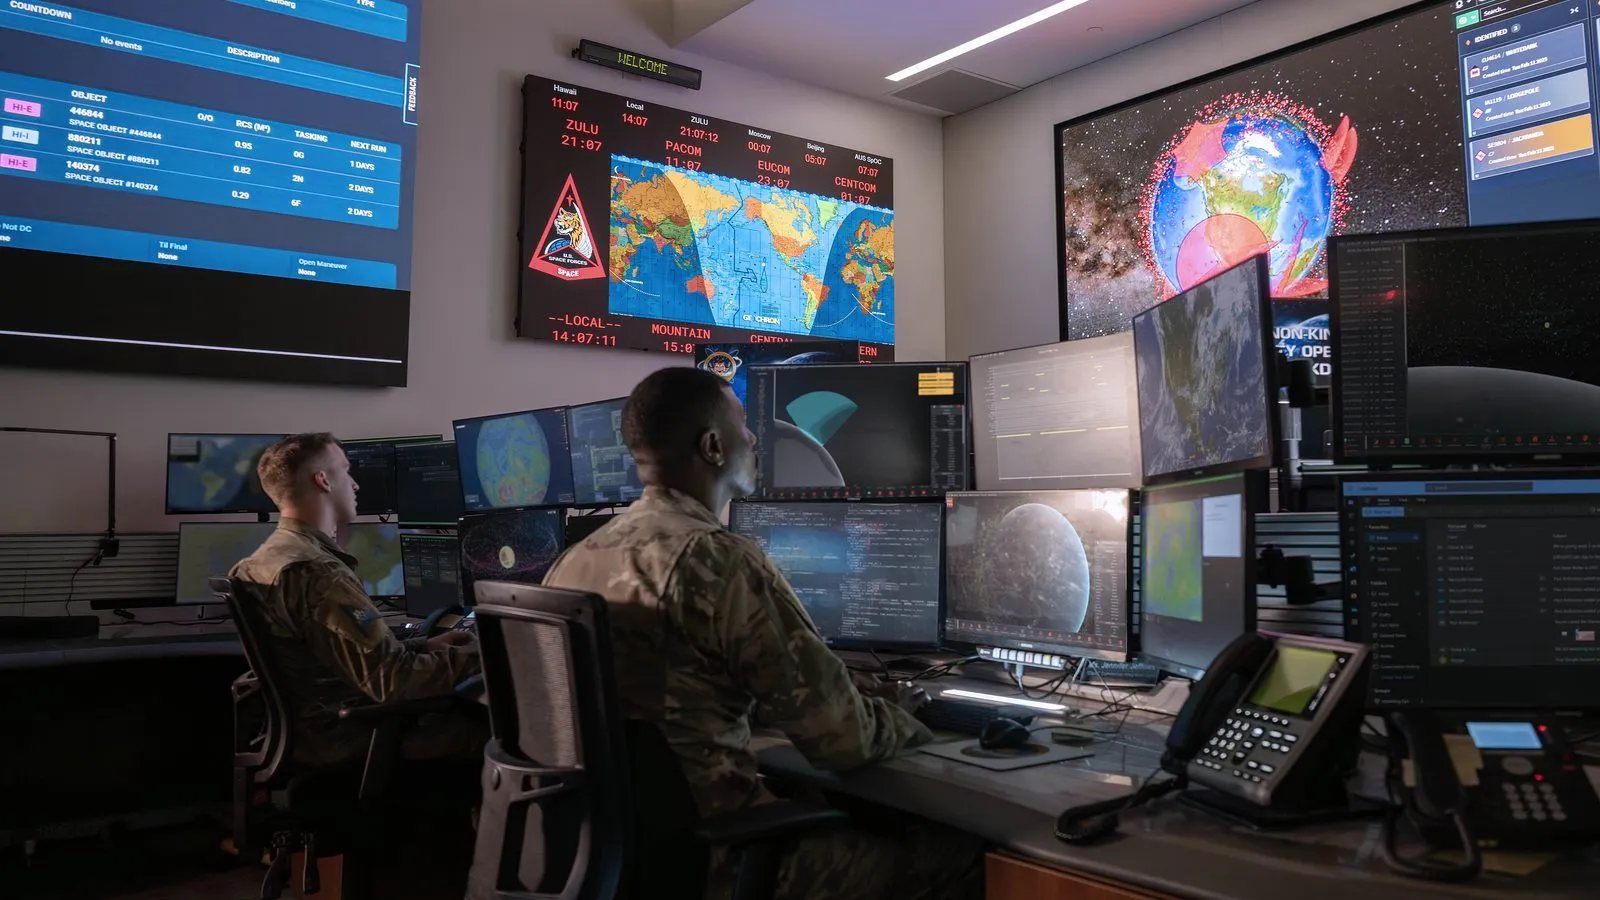
OpenAI president Greg Brockman described pointing Astra at OpenAI's own production systems until it ran out of vulnerabilities to find. “We took 25% of our production engineers and said, ‘Sorry, all your projects are on hold. You are now defending... You're going to use the models to find all the holes,’” Brockman said. The effort found and fixed a number of serious issues before saturating — reaching, in OpenAI's assessment, all of the critical problems Astra was capable of finding. The initiative reportedly grew out of an internal security sprint that mobilized more than 250 people across hundreds of service areas with incident-response-level urgency.
A Defense Factory connects AI agents to existing security and developer tooling — GitHub, GitLab, Snyk, Semgrep, Tenable, Jira, Linear, ServiceNow and others, via APIs, command-line tools and Model Context Protocol integrations — and runs them through five stages: inventorying systems that need assessment, discovering potential vulnerabilities, dynamically validating which ones are real, assigning clear ownership for remediation, and verifying the fix afterward.
For managed service providers, the relevant question isn't how to run offensive security tooling — it's how to govern access to increasingly capable defensive AI models on customer-facing infrastructure. That means treating high-capability security modes the same way any other elevated-privilege tool is treated: gated behind change control, requiring ticket and dual approval before activation on a managed tenant, with action logs retained and reviewable. OpenAI's own framing — using frontier models to close security gaps before attackers get equivalent tools — only holds up for a defender if the access controls around that capability are as tight as the capability itself.
This is a real, substantial security operations concept from OpenAI, not rumor or social-media chatter — the company published a full playbook alongside the announcement. MSPs evaluating AI-assisted vulnerability management should look at the governance model as closely as the capability, since the same continuous-scanning approach that finds bugs faster can also create a new elevated-access surface if it isn't controlled carefully.
Sources: OpenAI, Cybersecurity News.