





















01
Necessary Always on
Required for the site to work (login, preferences, security). Always on.
CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway, missed its 17 September CISA deadline. A single crafted email can hand an attacker root, no login required.
A critical flaw in Cisco's Secure Email Gateway has now blown past the deadline U.S. authorities set for fixing it. CVE-2026-76461 is a SQL injection vulnerability in the AsyncOS software that runs the gateway, and the U.S. Cybersecurity and Infrastructure Security Agency added it to its Known Exploited Vulnerabilities catalog on 14 September 2026 — the same day Cisco disclosed it — because attackers were already exploiting it before the advisory existed. The federal remediation deadline was 17 September; it has passed.
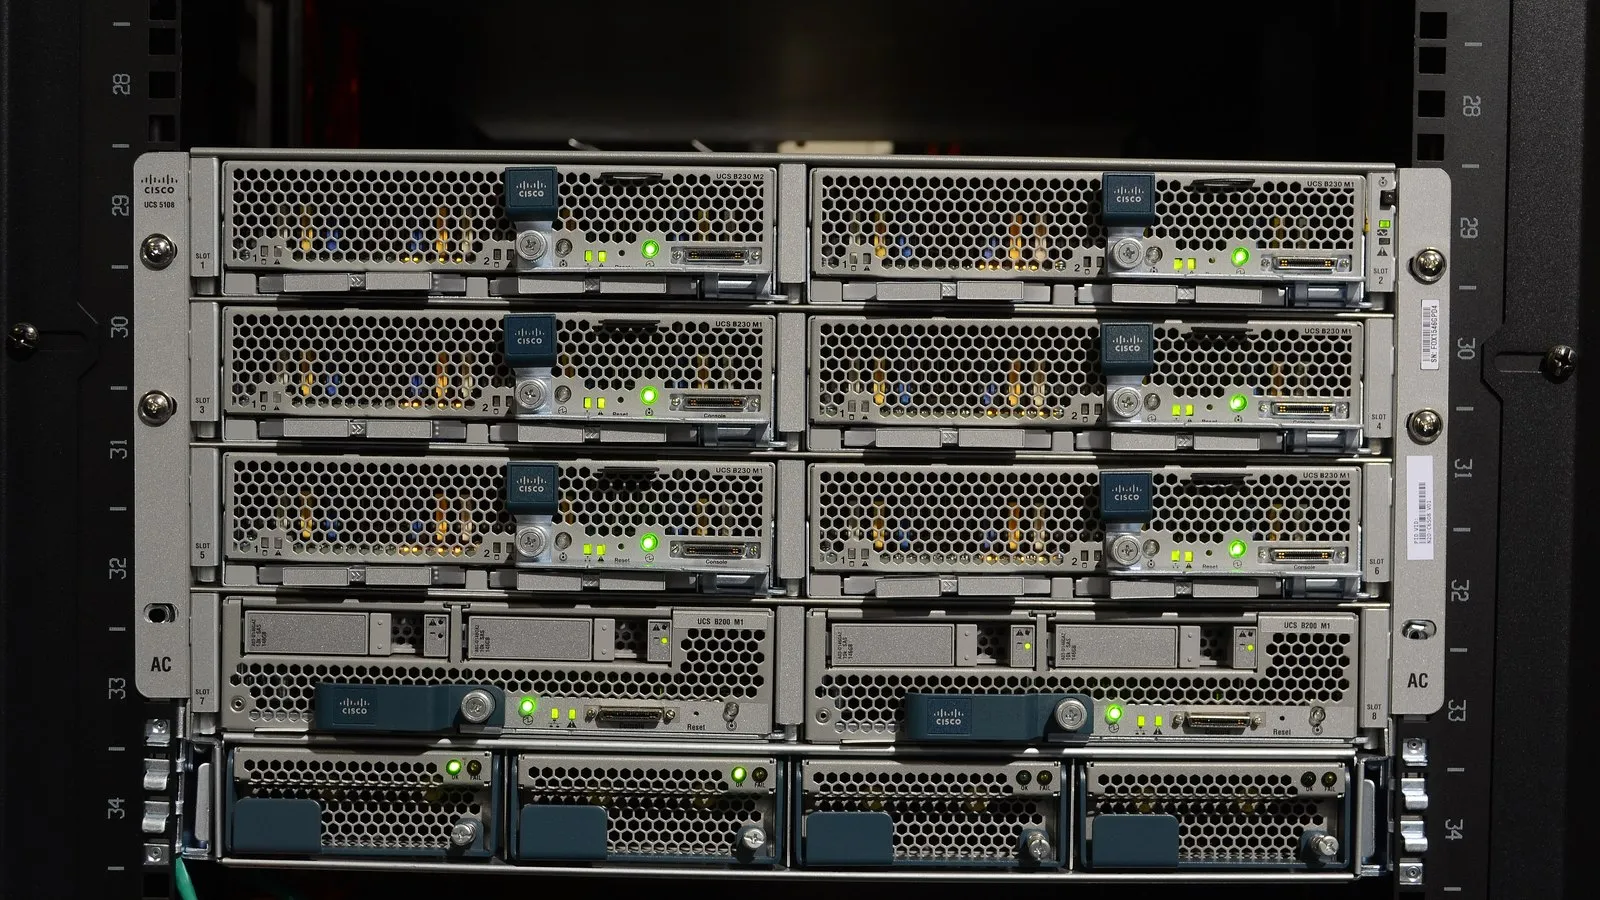
The vulnerability sits in how AsyncOS parses inbound email. A remote attacker with no credentials can trigger it simply by sending a specially crafted email through a vulnerable gateway — the appliance's normal job of processing mail is the attack surface. Successful exploitation leads to arbitrary SQL execution and, from there, command execution with root privileges on the underlying system. It affects both physical and virtual appliances, on-premises and cloud-hosted alike; Cisco has already upgraded every Secure Email Cloud device to a fixed build and separately contacted cloud customers whose gateways showed signs of malicious activity. Secure Email and Web Manager and Secure Web Appliance are not affected.
Cisco's fixed releases are AsyncOS 15.5.5-0141, 16.0.4-3021 and 16.5.0-780, with Cisco recommending the 16.5.0-780 line specifically — the 16.0.4-3021 build closes this bug but not four other critical issues covered in a companion hardening advisory. Because a compromised gateway can let an attacker erase its own trail, defenders should not rely solely on on-box logs; correlating with external firewall and network telemetry gives a more reliable picture. Cisco and outside researchers point to the gateway's mail logs as a starting point, looking for SQL statements that should never appear in normal message processing.
Every Secure Email Gateway appliance still on an unpatched AsyncOS build is exposed to unauthenticated compromise triggered by a single crafted email — there is no login screen standing between an attacker and the flaw. Inventory every gateway across managed estates, apply 16.5.0-780 (or the equivalent fix for a given train), and review mail logs for signs of prior exploitation before treating the appliance as clean.
Sources: Rapid7, SecurityWeek, CISA.