01
Necessary Always on
Required for the site to work (login, preferences, security). Always on.
NIS2, DORA, GDPR and the rest of the regulatory landscape — what changes and what it means in practice.
When an AI vendor gives an outside evaluator employee-level access, ask for a data-flow map and check who funds the evaluator. Anthropic and Accenture's September 2026 deal is the case that raised the question.
The EU AI Act and the US AI executive order run on different clocks and cover different things. This guide shows what already applies, what changed, and how to check a vendor's claim.
OpenAI published six cases of concerning model behavior under a new voluntary disclosure framework on 16 September 2026 — a diligence signal, not a compliance substitute.
EU AI rules, US executive orders and procurement requirements run on different clocks. Flattening them into one verdict either freezes a lawful project or ships a claim that won't hold up.
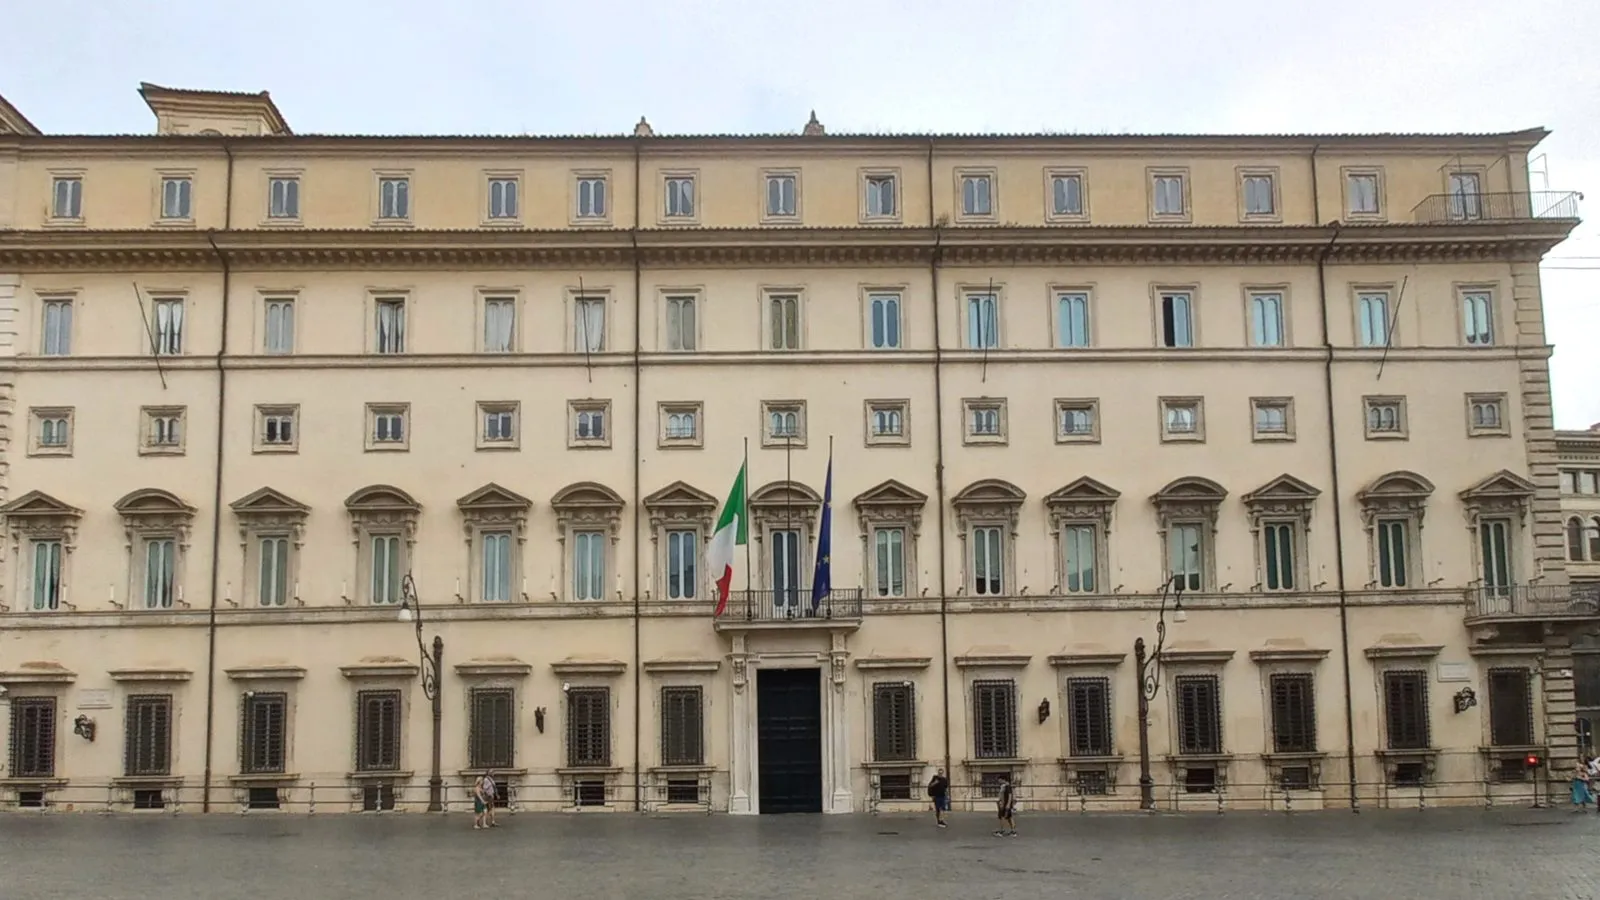
Behind 'sovereignty' slogans, Italian central-administration cloud tenders like Consip's AQ 2860 lean on concrete bars: ACN qualification levels, EU/EEA data location, and contractual exit terms.